The Countdown to Q-Day: Why Post-Quantum Cryptography Migration Is the Biggest Conversation in InfoSec Today
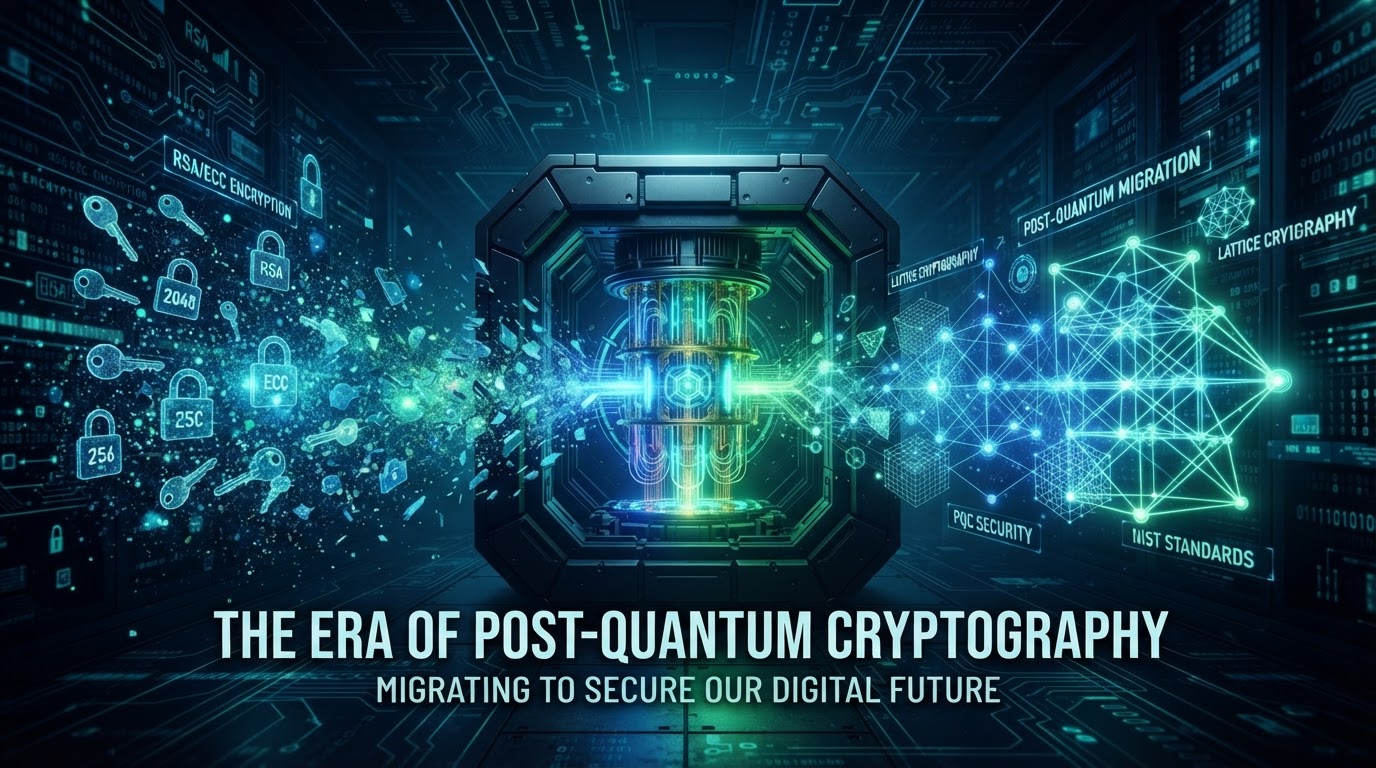
NIST has finalized its first post-quantum cryptography standards (FIPS 203, 204, 205), and the race to migrate every system on Earth off RSA and ECC is now the single biggest topic in the infosec and emerging tech industries.
The threat isn't theoretical — it's 'harvest now, decrypt later,' where adversaries are stockpiling encrypted data today to crack once a cryptographically relevant quantum computer arrives.
Office of Management and Budget has ordered federal agencies to complete PQC inventories by 2025 and begin migration by 2030.
NSA's CNSA 2.0 mandate requires national security systems to adopt PQC.
Google, Apple, Signal, and Cloudflare have already shipped post-quantum key exchange into production.
But the real challenge isn't the math — it's the inventory.
Most organizations don't even know where their cryptographic assets live, let alone which ones depend on algorithms that won't survive Q-Day.
Here's a full breakdown of the NIST standards (ML-KEM, ML-DSA, SLH-DSA), the harvest-now-decrypt-later threat model, the NSA CNSA 2.0 timeline, what the major tech players have already shipped, and why cryptographic agility — not just algorithm replacement — is the real skill the industry is hiring for in 2026 and beyond.
Ready to put this into practice?
Explore the hands-on labs and tools mentioned in this article.
Get Started